IT Governance Best Practices: 10 Priorities for 2026
The most popular advice about IT governance is to start with a committee, a framework, and a policy library. That's backward if nobody can explain who may approve a technology purchase, accept a security risk, or stop a failing project. More documentation won't fix decisions that executives routinely bypass.
For a fractional or newly appointed CIO, the immediate task is to make technology decisions visible, enforceable, and connected to business outcomes. A useful governance process tells a department head where to take a request, tells IT what evidence to collect, and tells leadership when intervention is necessary. It also lets routine work proceed without executive permission.
Practical rule: Don't introduce a governance requirement unless you can identify the decision it changes, the person accountable, and the evidence that proves it happened.
The IT governance best practices below follow a build sequence, not a maturity contest. Establish a common framework and decision rights first. Use those foundations to govern investments, risk, suppliers, and spending, then strengthen reporting and emerging-technology controls.
Use your opening ninety-day plan to establish this operating rhythm rather than attempting enterprise-wide perfection. Start with the decisions causing the most friction or exposure, apply controls proportionate to the risk, and expand when owners can demonstrate that the process works. An urgent security incident or uncontrolled AI deployment still takes priority over the sequence.
1. Adopt a Recognized IT Governance Framework
Use a framework as a reference model, not an implementation backlog. A newly appointed CIO needs a consistent way to connect business expectations, technology responsibilities, and control evidence without inventing terminology for each department.
ISACA's history of COBIT describes how the framework evolved toward enterprise governance, with COBIT 2019 defining 40 governance and management objectives. That breadth is useful for coverage, but it isn't a reason to implement everything simultaneously.
Start with the decisions under pressure
Say a regional healthcare organization has inconsistent supplier reviews and unreliable recovery testing. Start with objectives relevant to those exposures, map existing controls, and identify missing owners or evidence.
- Reuse existing work: Link current contracts, recovery exercises, and approval records to the selected objectives.
- Set proportionate targets: Require stronger evidence for critical clinical systems than for a low-impact internal tool.
- Name accountable owners: Give each adopted objective an owner with authority to resolve gaps.
Keep governance separate from service-management execution. Governance determines priorities and acceptable risk; practices such as change enablement organize delivery. Guidance on implementing ITIL practices with SysAid can complement that operational layer, but a service-management tool doesn't replace executive accountability.
2. Define Clear IT Decision Rights and Accountability
A sales leader buys an AI-enabled application, procurement negotiates the contract, and IT discovers the integration afterward. The problem isn't merely shadow IT. Nobody established which decisions required technology, security, legal, or business approval.
Document decision rights before creating additional committees. A RACI matrix helps identify contributors, but it needs approval thresholds, escalation routes, and an explicit owner for residual risk.
Evidence from KPMG's Global AI Pulse survey, covering 2,145 senior leaders across 20 countries, found that only about one-third said AI governance roles, responsibilities, and processes were very clear and well managed.
Separate advice from authority
For an application purchase, the business sponsor should own the intended outcome, IT should assess architectural fit, security should assess exposure, and procurement should own commercial execution. An authorized executive must accept unresolved business risk rather than leaving that decision implicitly with the technical reviewer.
Use your organization's CIO and CISO responsibilities to clarify where delivery authority and security oversight differ.
- Delegate routine decisions: Preapprove purchases that meet agreed commercial, architecture, and data-handling conditions.
- Escalate material exceptions: Route sensitive-data access or critical-service dependencies for deeper review.
- Record the decision: Capture the approver, conditions, evidence, and review trigger.
For fractional leaders, name an internal delegate who can act between engagements. Accountability can't depend on the adviser being available.
3. Align IT Portfolio Management with Business Outcomes
A project list isn't a portfolio. It becomes a portfolio when executives compare competing investments, acknowledge resource constraints, and stop work that no longer deserves funding.
Build an inventory of applications, services, and active initiatives using finance records, procurement data, identity-provider integrations, and interviews with business owners. Mark uncertain entries rather than postponing review until every field is complete.
Compare outcomes, not presentation quality
Say operations requests warehouse connectivity improvements while marketing requests a customer analytics platform. Compare their business outcomes, dependencies, delivery capacity, ongoing costs, and risk reduction using the same criteria.
- Name the benefit owner: Identify who will verify fewer shipping delays or better campaign decisions after implementation.
- Expose dependencies: Show whether the analytics proposal requires data cleanup that hasn't been funded.
- Include retirement: Identify which existing application, contract, or manual process will disappear.
- Fund the full lifecycle: Include implementation, support, security, integration, and eventual exit.
Weighted scoring can make trade-offs explicit, but don't pretend the final score makes the decision. Executives may prioritize a mandatory resilience investment over an attractive growth initiative, provided they document why.
Review delivery capacity alongside money. A portfolio can fit the budget while overwhelming the same integration engineers and business subject-matter experts.
Approving a project without identifying what will stop, wait, or receive fewer resources isn't prioritization.
The useful output is a funded sequence with named owners, not an increasingly polished collection of business cases.
4. Integrate IT Risk into Enterprise Risk Management
An unsupported database is a technical condition. An inability to process orders during a prolonged outage is a business risk. Report both, but ask executives to make decisions about the business consequence.
Use the enterprise risk register rather than maintaining an unrelated technology register with incompatible scoring. Describe the affected service, plausible failure scenario, existing safeguards, remaining exposure, and required decision.
Make risk acceptance explicit
Suppose a manufacturer can't replace an aging production-control platform before its busiest season. IT can propose network isolation, restricted administration, tested backups, and vendor support arrangements, but an authorized business executive must accept the remaining operational exposure.
Record that acceptance with:
- A defined scope: Specify the systems and business activities covered.
- Compensating controls: Identify safeguards and the evidence needed to verify them.
- An expiration trigger: Require reassessment after a material change or agreed review date.
- A funded action: Assign responsibility and resources for the longer-term remedy.
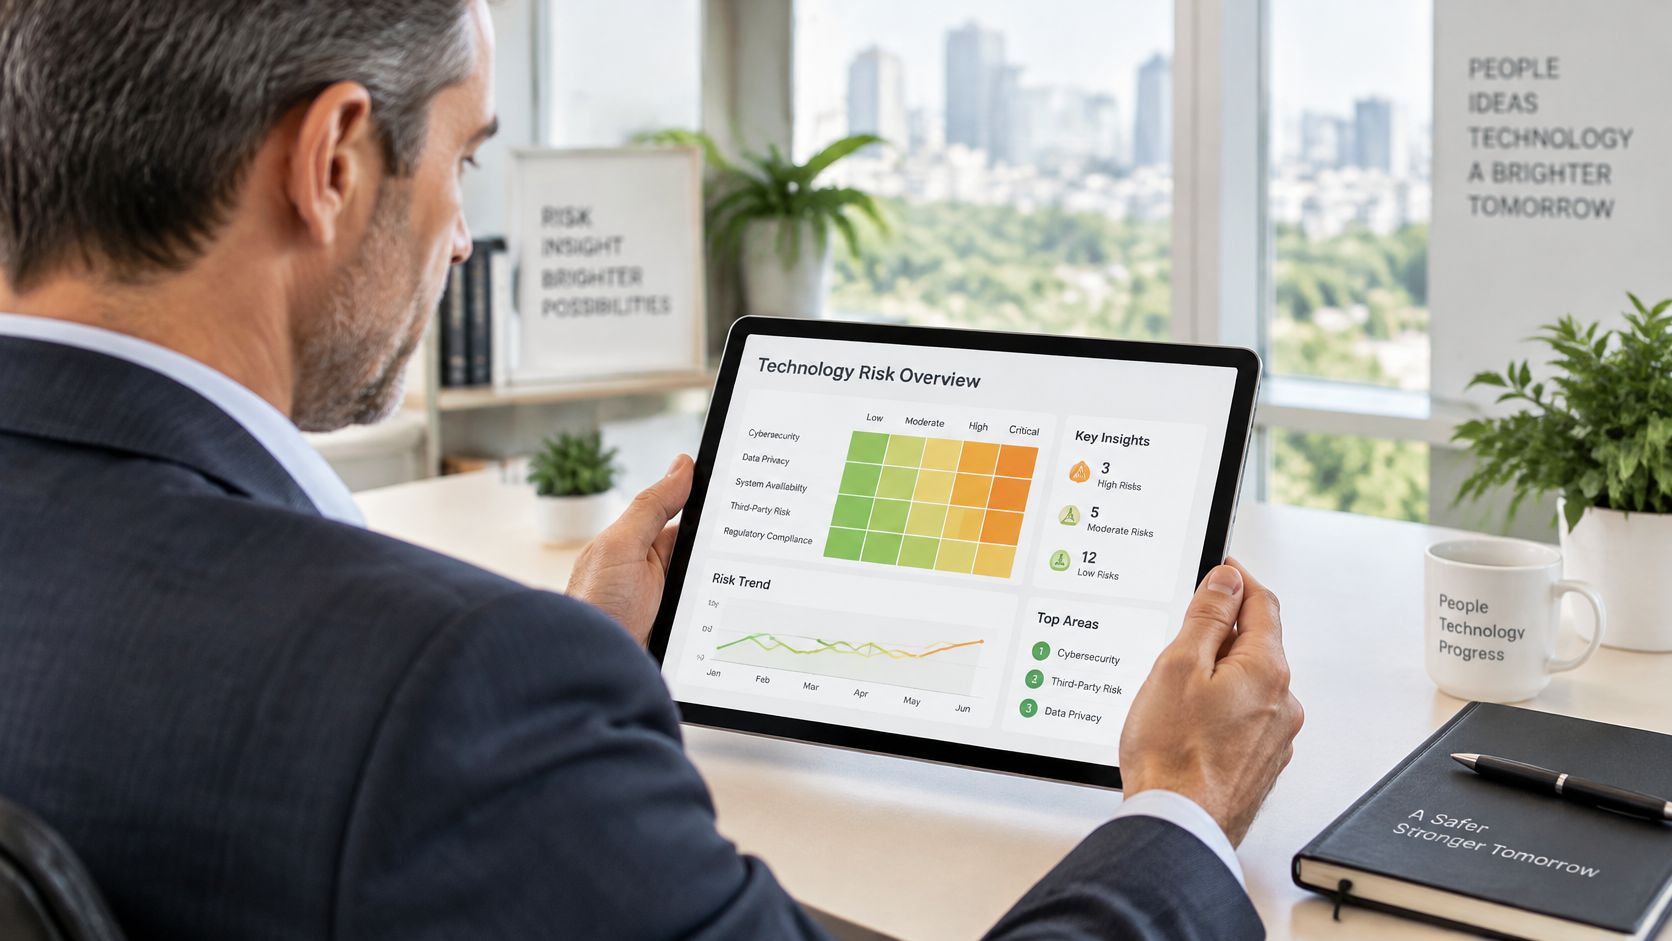
Don't let a risk heat map substitute for the scenario. A red square doesn't explain whether leadership should fund replacement, change operating procedures, transfer exposure, or accept it.
Use a common likelihood-and-impact scale, but acknowledge uncertainty. Where financial estimates are weak, state assumptions and show the operational consequences instead of manufacturing precise loss figures.
5. Govern Cybersecurity Using the NIST Cybersecurity Framework 2.0
Security governance should explain why safeguards match business exposure, not just how many tools the organization operates.
NIST's Cybersecurity Framework materials describe CSF 2.0's addition of the Govern Function alongside Identify, Protect, Detect, Respond, and Recover. Govern brings organizational context, risk strategy, responsibilities, policy, oversight, and supply-chain considerations into the security conversation.
Build profiles around critical services
For a distributor, start with order processing, warehouse operations, and customer communications. Develop a Current Profile from evidence of existing practices, then a Target Profile reflecting the business's required resilience and risk tolerance.
A recovery requirement should lead to a tested restoration procedure and accountable service owner. An identity requirement should lead to enforceable access controls and review evidence, not merely a policy statement.
- Prioritize consequential gaps: Address weaknesses that could interrupt critical services or expose sensitive information.
- Include suppliers: Evaluate dependencies on identity providers, hosting platforms, and managed services.
- Measure effectiveness: Track restoration results, overdue remediation, and coverage of critical assets.
Avoid turning every framework outcome into an independent project. A shared identity improvement may address several requirements, while a documented policy may satisfy none without implementation.
Use a comparison of cybersecurity compliance frameworks to distinguish governance needs from contractual or regulatory obligations. Mapping requirements can reduce duplicate evidence collection, but it doesn't make different obligations interchangeable.
6. Implement Third-Party and Vendor Governance
The cheapest proposal can become the most expensive dependency. Before selecting a provider, establish how the organization will monitor performance, investigate incidents, retrieve its data, and leave.
Tier suppliers by business criticality, data access, privileged access, integration depth, and replacement difficulty. A provider administering production infrastructure warrants deeper review than a tool containing public marketing assets.
Negotiate the exit before signing
Say a business is replacing its contact-center platform. Procurement should evaluate more than licensing and implementation fees: number portability, recording exports, integration support, outage communications, and transition assistance all affect the eventual operating risk.
- Define service commitments: Specify measurement methods, exclusions, escalation contacts, and remedies.
- Clarify data handling: Document access, storage, subcontracting arrangements, return formats, and deletion evidence.
- Test portability: Confirm that exported records remain usable outside the platform.
- Assign an internal owner: Keep responsibility for performance and unresolved issues inside the business.
Use IT vendor management best practices to connect selection diligence with ongoing oversight. A completed questionnaire isn't proof that the provider continues to meet your requirements.
Review incidents, service performance, unresolved actions, consumption, and upcoming contractual decisions together. Increase scrutiny when a supplier changes ownership, introduces material subprocessors, or expands access.
Don't apply identical reviews to every supplier. Excessive low-risk diligence consumes the attention needed to challenge providers whose failure would materially disrupt operations.
7. Establish IT Financial Management and Technology Expense Governance
Start by showing business leaders what services cost and why. Showback usually provides a better starting point than chargeback, because disputed allocations can distract from fixing poor consumption visibility.
Map invoices and ledger entries to services, business owners, contracts, and cost drivers. For cloud workloads, use enforceable tags for ownership, environment, application, and cost allocation, with a process for resolving unassigned resources.
Separate savings from cost displacement
Suppose an engineering team reduces cloud storage expense by shortening retention. That's only a sound decision if the new retention period still meets recovery, operational, and legal requirements.
Pair spending reviews with service and business measures:
- Cloud consumption: Examine idle resources, oversized workloads, storage growth, and commitment utilization.
- Software licensing: Compare purchased entitlements with actual use and contractual reassignment rules.
- Communications expenses: Reconcile circuits, devices, locations, and invoices before renewing.
- Unit economics: Track cost per relevant business transaction where the denominator is reliable.
FinOps can organize cloud collaboration, while Technology Business Management can provide a service-oriented cost model. Neither requires you to delay useful reporting until every allocation is exact.
Document allocation assumptions and let business owners challenge them. An approximate, transparent service cost is more useful than an apparently precise figure nobody can reconcile.
Approve savings initiatives with an owner and verification method. Removing licenses from a spreadsheet doesn't reduce expenditure until someone changes the entitlement or commercial commitment.
8. Maintain a Living IT Policy and Standards Framework
A policy requiring approval for every production change sounds controlled. If routine changes wait in a queue until engineers bypass the process, the policy isn't governing the work effectively.
Keep policy, standards, and procedures distinct. Policy states the obligation, standards define required conditions, and procedures explain execution in the actual environment.
Grant Thornton's AI Impact Survey found that only 20% of surveyed organizations had a fully defined AI-incident-response playbook with assigned owners that had been tested through tabletop exercises. Written intent and tested operating capability aren't the same.
Make compliance executable
For change management, define preauthorized standard changes, risk-assessed normal changes, and an emergency route with retrospective review. Link the approval record, deployment evidence, rollback instructions, and outcome in the service-management workflow.
- Assign ownership: Give every policy an accountable owner and review trigger.
- Manage exceptions: Record scope, rationale, compensating controls, approver, and expiration.
- Test procedures: Exercise incident escalation and recovery instructions with the people expected to execute them.
Control-design test: Ask an operator to follow the procedure using only the published instructions. Missing access, unclear authority, and outdated contacts are governance defects.
Train employees on realistic decisions, such as entering customer data into an unapproved assistant. An attestation records acknowledgment; it doesn't demonstrate that someone can apply the rule.
9. Use Metrics, KPIs, and Board-Level IT Reporting
The board doesn't need a service-desk export. It needs to understand whether technology supports strategy, where exposure exceeds tolerance, and which decisions require its attention.
In Deloitte's 2025 survey of 695 board members and C-suite executives across 56 countries, 66% reported that their boards had limited to no AI knowledge or experience. Reporting therefore needs business context and targeted education, not unexplained technical terminology.
Organize reporting around decisions
Say a critical customer platform has met its availability target while recovery testing has failed. A green uptime indicator alone would hide the resilience decision leadership needs to make.
Present a concise dashboard supported by drill-down evidence:
- Business value: Benefits realized against the approved investment case.
- Reliability: Critical-service disruption and recovery-test results.
- Risk: Material exceptions, overdue remediation, and accepted exposure.
- Financial control: Forecast changes, consumption trends, and renewal commitments.
- Decisions required: Funding, reprioritization, exception acceptance, or escalation.
Define each metric's calculation, source, owner, target, and reporting period. Show trends and explain changes in scope so an improving result doesn't merely reflect excluded assets.
Avoid rewarding activity alone. Training completion, vulnerability scans, and projects launched are useful operational measures, but executives also need evidence of changed behavior, reduced exposure, and realized benefits.
Retire metrics that never influence action. Keep operational detail available without making directors sift through it.
10. Apply Data and AI Governance Standards
A SaaS renewal can add AI capabilities without a separate procurement project. Fractional and newly appointed CIOs should first establish a reliable inventory of tools, including embedded assistants, external models, internal applications, and autonomous agents. A product's AI label is not a sound basis for deciding whether it needs governance.
Govern actions as well as outputs
An agent that drafts customer-service replies needs different permissions from one that issues refunds or changes account records. Set boundaries for each action, including when a person must approve it and what activity gets monitored.
Start with a few controls that support real decisions:
- Assign data owners: Specify permitted uses, access, quality expectations, and retention.
- Classify use cases: Weigh data sensitivity, customer impact, reversibility, and the degree of autonomy.
- Set deployment gates: Require an accountable owner, approved data boundaries, logging, rollback procedures, and incident handling before release.
- Monitor behavior: Compare actual actions with approved permissions and investigate deviations.
Apply the same discipline to conventional software. For an approved mailX email deliverability toolkit, record its permitted use, the data it can access, the scope of user access, and the accountable owner. A focused approval like this keeps a routine SaaS deployment governed without turning it into a paperwork exercise.
An agent can produce a correct answer while using data it was not authorized to access. Govern both the result and the actions that produce it.
How the 10 IT governance practices differ in artifacts, trade-offs, and sources
| Item | Core Artifact | Main Trade-off | Standard or Source |
|---|---|---|---|
| Adopt a Recognized IT Governance Framework | Tailored governance framework with objectives and maturity targets | Shared accountability and audit readiness versus implementation effort and paperwork | COBIT 2019; ISO/IEC 38500:2024 |
| Define Clear IT Decision Rights and Accountability | RACI matrix, governance bodies, and escalation paths | Faster, clearer decisions versus approval delays or excessive centralization | Weill and Ross; ISACA COBIT |
| Align IT Portfolio Management with Business Outcomes | Investment inventory, scoring model, and review cycle | Better strategic prioritization versus data demands and potentially political scoring | PMI portfolio management standard; ISACA COBIT APO |
| Integrate IT Risk into Enterprise Risk Management | Enterprise risk register with owners and treatment plans | Board-level visibility versus difficulty quantifying risks and sustaining follow-through | COSO ERM; ISO 31000; ISACA Risk IT |
| Govern Cybersecurity Using the NIST Cybersecurity Framework 2.0 | Cybersecurity profiles organized around six core functions | Flexible, recognized security guidance versus effort to map controls; no standalone certification | NIST Cybersecurity Framework 2.0 |
| Implement Third-Party and Vendor Governance | Vendor risk assessments, contract safeguards, and performance monitoring | Reduced supplier risk versus assessment burden and ongoing resource needs | Shared Assessments SIG; ISO/IEC 27036 |
| Establish IT Financial Management and Technology Expense Governance | Cost allocation, showback or chargeback, and spend reporting | Greater cost visibility versus allocation disputes and setup effort | TBM Council; FinOps Foundation |
| Maintain a Living IT Policy and Standards Framework | Owned and regularly reviewed policies, standards, and procedures | Consistent, auditable practices versus policy upkeep and risk of excessive documentation | ITIL 4; ISO/IEC 27001 |
| Use Metrics, KPIs, and Board-Level IT Reporting | Balanced scorecard, defined KPIs, and executive dashboards | Better oversight and decisions versus reporting fatigue and metric gaming | Kaplan and Norton Balanced Scorecard; ISACA COBIT MEA |
| Apply Data and AI Governance Standards | Data stewardship model, AI inventory, and risk controls | More trustworthy, accountable data and AI versus evolving standards and enforcement challenges | ISO/IEC 42001:2023; NIST AI RMF 1.0; DAMA-DMBOK |
Turning Ten Practices Into a Governance Rhythm
Governance holds only when leaders use it on a schedule and act on the results. Begin by naming owners for decision rights and the most consequential technology risks, then establish a recurring review covering portfolio, vendors, spending, and performance together. Expand the scope when that review consistently produces decisions and closes actions.
For a fractional CIO, continuity matters as much as meeting design. Assign an internal coordinator who maintains the decision log, gathers evidence, tracks exceptions, and follows up between executive sessions. The business must retain the ability to operate the process without waiting for its adviser.
Establish the operating sequence
During the opening month, concentrate on visibility and authority. Identify critical services, active initiatives, material suppliers, unresolved risks, and imminent renewals, then confirm who can approve, defer, reject, and accept exceptions.
During the following month, apply the process to live decisions. Select a consequential renewal, an investment competing for resources, and a material control gap; use them to test whether the approval routes and evidence requirements are practical.
During the final month of the initial plan, review outcomes rather than document completion. Check whether decisions were followed, controls generated evidence, suppliers met commitments, and business owners could explain the value received.
- Before each review: Distribute exceptions, changed risks, investment choices, and recommended actions.
- During the review: Resolve trade-offs and record accountable owners, conditions, and due dates.
- Between reviews: Escalate material incidents or threshold breaches immediately.
- After the review: Verify completion using evidence rather than verbal assurance.
Keep the operating record simple enough to maintain. A shared decision register linked to contracts, risk records, project information, and service-management evidence can be sufficient initially. Buying a governance platform before agreeing on ownership and workflow gives unresolved ambiguity a new interface.
Keep the control that changes behavior. Simplify the document that merely describes it.
Review the governance process itself. Look for approvals that add no scrutiny, exceptions that never expire, reports nobody challenges, and action items repeatedly carried forward without intervention.
Don't remove a required control merely because it's inconvenient. Instead, identify whether automation, clearer delegation, reusable evidence, or a better standard can achieve the same objective with less friction.
The test is straightforward: can leadership explain what it funded, what risk it accepted, who owns delivery, and whether the expected outcome occurred? If those answers are clear and supported by evidence, governance is becoming part of management rather than a parallel paperwork exercise.
MR2 Solutions offers vendor-neutral technology evaluation, procurement, implementation, and ongoing governance, supported by fractional CIO and CISO leadership. Visit MR2 Solutions to discuss your decision rights, supplier oversight, and technology investment priorities, and build a governance rhythm your internal team can sustain.