SD WAN Use Cases: 8 Proven Examples for 2026
What if the vendor is not the decision that's breaking your WAN project? Ask ten network teams what SD-WAN use cases matter and you'll get ten answers, from MPLS replacement and cloud acceleration to store rollouts and call quality. That ambiguity is exactly why deployments disappoint. Teams buy a platform, then discover the design that helps a retailer open stores doesn't solve a clinic's segmentation problem or a contact center's jitter problem.
Treat each use case below as a replicable deployment pattern, not a feature. Every pattern needs its own transport mix, policy model, pilot test, and KPI. A broadband circuit that's fine for guest Wi-Fi can ruin voice. A local internet breakout that speeds Microsoft 365 can create a security gap if inspection isn't consistent.
Identify the pattern that matches your highest cost, risk, or user complaint first. Then pressure-test vendors against that pattern in a pilot, with links pulled, policies changed, and applications measured under load. I recommend starting with one proven pattern, proving the numbers at representative sites, and only then scaling the template across the estate.
1. Hybrid WAN and Transport Bonding for Multi-Site Branches
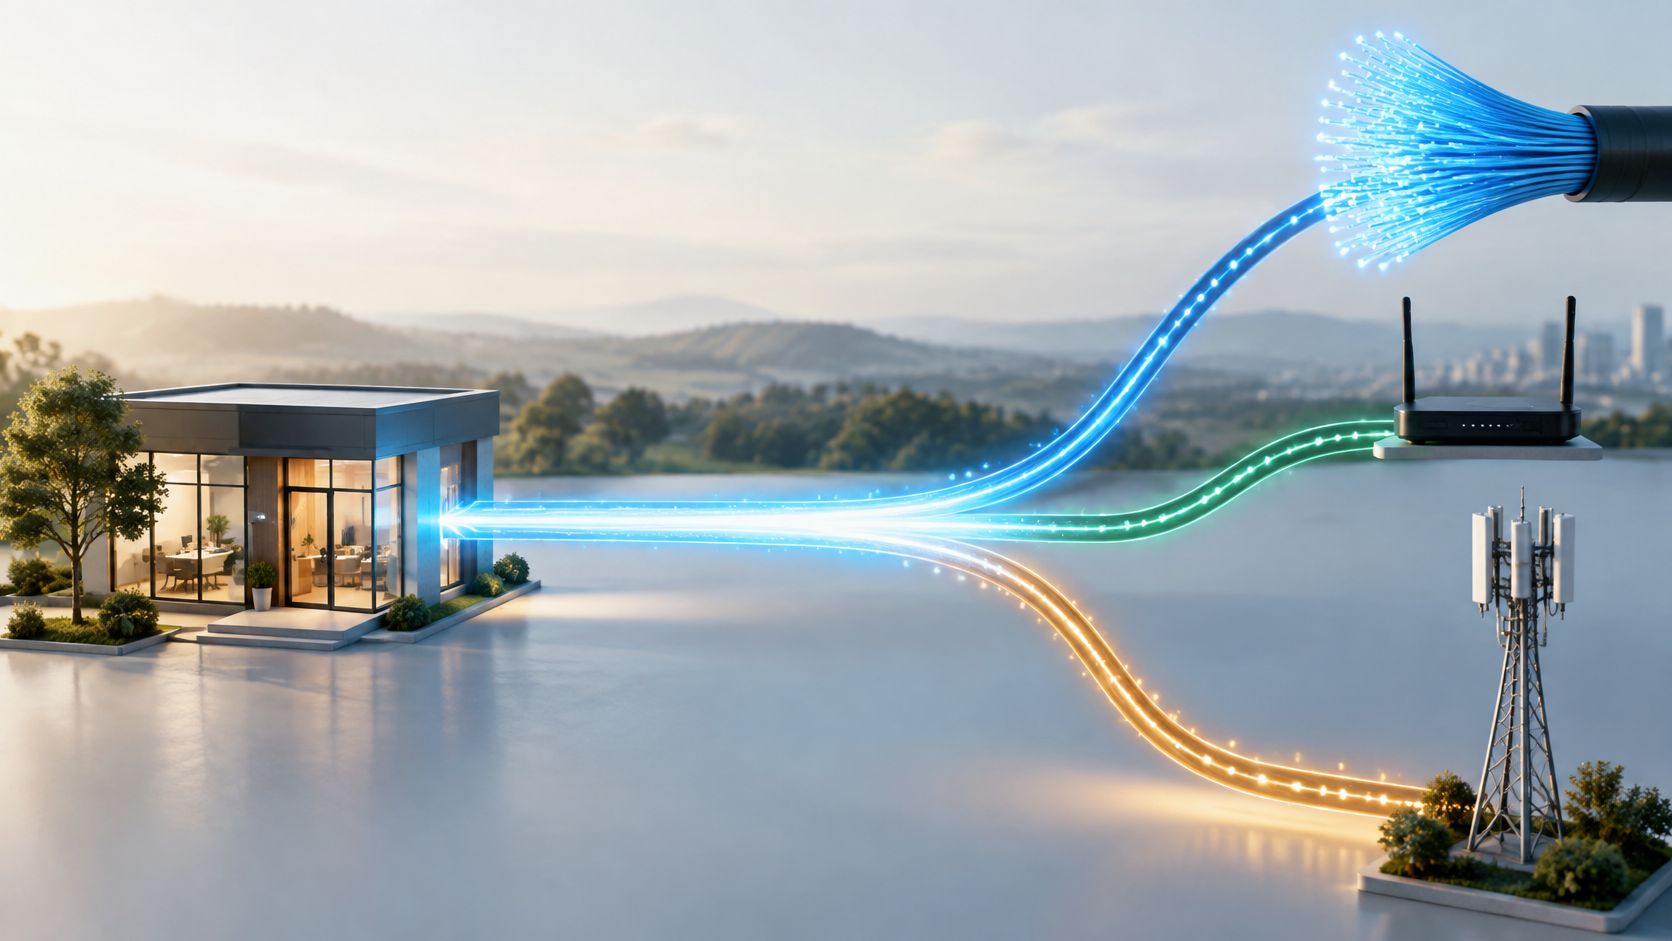
Most branch networks were built around one expensive private circuit. This pattern replaces that single bet with an overlay across MPLS, broadband, fiber, and LTE or 5G, steered per application by live latency, jitter, and packet loss. The IDC Communications and Networking Survey conducted in 2022 with more than 1,200 respondents found the leading expected benefit was the flexibility to use a network mix by offloading some MPLS traffic onto the internet.
Say a regional retailer keeps a small MPLS or dedicated circuit for payments at flagship stores, uses dual broadband for inventory and cloud apps, and adds LTE for failover. A professional services firm can bond two broadband circuits for VoIP and file sharing, provided the carriers don't share the same physical path into the building. Diversity on an invoice isn't diversity in the ground.
Pilot Checks That Matter
- Baseline first: Record current MPLS spend, peak utilization, and top applications per site before you choose transports.
- Map SLAs to policy: Define acceptable latency, jitter, and loss for voice, video, and ERP, then tie each class to a preferred and fallback path.
- Pull each link: Test hard failure and brownout separately, because a degraded link that stays up is harder to handle than a clean cut.
Protect the local side too, including how you protect WiFi across office locations, since a resilient WAN won't help users on a weak branch LAN. KPIs to track are usable application throughput, failover time, loss during congestion, and cost per site. Circuit capacity alone tells you almost nothing.
2. Cloud-First Direct Internet Access for SaaS and Microsoft 365
Backhauling Microsoft 365 through headquarters made sense when applications lived in your data center. It doesn't now. This pattern sends trusted SaaS traffic directly from the branch to the internet, while legacy or sensitive traffic stays on the encrypted overlay to a hub or security service.
A multi-site professional services firm, for example, can break out Teams and SharePoint locally and measure call setup and file sync before and after cutover. A healthcare group can send SaaS EHR portal traffic locally through inspected breakout, while older clinical systems still ride a private path. The trade-off is clear. You cut hub bandwidth and latency, but every breakout becomes an entry point that needs firewalling, DNS security, and logging.
Adoption moved fast for this reason. An IDC U.S. SD-WAN survey from November 2019 of 1,223 respondents found 41.8% had already deployed SD-WAN and 40.2% planned deployment within 12 months. Don't treat that momentum as permission to open breakout everywhere on day one.
Break out by application and identity, not by destination port alone. If you can't name the app, user group, and inspection point, don't break it out.
Follow Microsoft's Microsoft 365 network connectivity guidance for endpoint categories, and review SaaS endpoint lists on a schedule because they change. Use application telemetry, synthetic Teams probes, and DNS logs to validate the change. Track SaaS response time, hub circuit utilization, blocked DNS queries, and help desk tickets per site. If latency improves but security events become invisible, you haven't improved the design.
3. SD-WAN with Integrated Security and SASE Architecture
Routing traffic efficiently is pointless if each branch enforces a different security rule. This pattern converges SD-WAN with next-generation firewalling, intrusion prevention, URL filtering, and secure web gateway functions, either at the edge or through cloud-delivered SSE as part of SASE.
Consider a financial services organization consolidating branch firewalls, web filtering, and SD-WAN into one managed platform. Or a public sector agency that needs identical policy at headquarters and small field offices. Both gain consistency, but both also face a governance question vendors often skip. Who approves segmentation and steering changes, who tests them, and where's the audit evidence?
That concern is now central. A 2025 North American customer survey summarized in recent market analysis found aligning network and security architectures across distributed branches was enterprises' top concern, while 92% preferred managed or co-managed SD-WAN. If your team is thin, that operating model decision matters as much as the platform.
Design Decisions to Make Early
Map existing NIST, HIPAA, or internal controls to SASE policy objects before migration, and decide where sensitive traffic gets inspected. Cloud inspection simplifies branch hardware but can add latency or data residency questions. Edge inspection keeps traffic local but means more lifecycle work per site.
Create joint network and security ownership, with change logging, rollback, and a clear answer for failover during a security service outage. For a direct comparison of architectures, see this guide to SD-WAN versus SASE. Track policy hit rates, inspection latency, blocked threats, and configuration drift. I recommend phasing SSE by site group rather than forcing a rip and replace that leaves legacy MPLS and cloud traffic under different rules.
4. Retail and Franchise Store Networking with Zero-Touch Provisioning
Retail exposes weak branch design faster than almost any other environment. Payments, point-of-sale, inventory, cameras, guest Wi-Fi, and digital signage compete on links managed by almost no on-site IT staff.
The pattern is a standard store template shipped as a preconfigured edge device. Staff plug it in, it calls the controller, pulls policy, segments payment traffic, and prioritizes POS over media. In a Cisco-documented fuel-retail deployment, SD-WAN increased store bandwidth by approximately 200% to 300% while supporting IP video surveillance and media streaming at pumps. The value wasn't raw speed. It was path diversity plus policy that kept forecourt and payment systems ahead of less critical traffic.
A quick-service franchise can use the same template with LTE backup so card transactions continue during a broadband outage. That only works if you've classified traffic before the outage. Payment and operational control get protected treatment. Guest Wi-Fi and streaming get what's left.
- Pilot the workflow: Ship devices to a small set of stores and time unboxing to first transaction.
- Test real failover: Pull broadband during trading simulation and measure transaction completion, not just link status.
- Stage template changes: Roll configuration updates in rings with an automatic rollback trigger.
- Watch store KPIs: Monitor transaction latency, payment success, uptime, packet loss, and camera upload impact.
Don't validate with a speed test at an empty flagship. Use a busy, ordinary store with the carrier mix you plan to deploy.
5. Healthcare Multi-Site Connectivity with Segmentation and Compliance Controls
A clinic cannot treat EHR, imaging, medical devices, voice, and guest Wi-Fi as one flat network. This pattern connects hospitals, outpatient clinics, labs, and imaging centers through encrypted overlays with separate segments for clinical, administrative, device, and guest traffic.
Say a health system connects outpatient clinics to a central EHR, isolates medical IoT with strict allow lists, and prioritizes telehealth and radiology transfers over general internet use. SD-WAN identifies those flows, applies service objectives, and steers them over the path meeting latency and loss thresholds. A case involving ATSU in a Netskope-published deployment summary reported PCI and HIPAA compliance support, application-performance assurance, flow-level visibility, and a claimed 10x reduction in total cost of ownership. Treat vendor case numbers as a prompt for your own baseline, not a forecast.
Controls Before Cutover
Document a data flow map for regulated traffic first. Which systems talk to which destinations, where is traffic inspected, and what evidence will an auditor ask for? Confirm business associate agreements where required, and test clinical failover during maintenance windows, not during clinic hours.
Practical rule: If a device cannot be patched or authenticated like a workstation, it belongs in its own segment with the shortest possible allow list.
Baseline carrier spend, site count, incident volume, mean time to diagnose, and EHR response time. After deployment, compare path quality, failover behavior, security event visibility, and operating cost. The win in healthcare is predictable access with centralized observability, not transport savings alone.
6. Cellular and LTE/5G Failover for Remote and Mission-Critical Sites
Some sites don't have good fiber. Others can't wait for it. Construction trailers, utility substations, pop-up clinics, and temporary offices often start with LTE or 5G as primary transport, then keep cellular as backup when wired service arrives.
A utility can place cellular-connected edge devices at remote substations for telemetry and management access. A construction firm can connect a field office over 5G in days, apply the same security template as headquarters, and move the kit to the next project. Both cases depend on signal reality, not carrier coverage maps.
Survey each site for signal strength, antenna placement, and interference before you commit. Check performance at busy times, because cellular throughput and latency vary by tower load. Where coverage is uncertain, use dual-carrier SIMs or dual modems and test both carriers under load.
Keep Cellular Costs Under Control
Reserve cellular for critical applications during failover. Let payments, VoIP, EHR, or SCADA management traffic move first, and block software updates, cloud backup, and guest Wi-Fi from consuming metered data. Set data caps, alerts, and policy-based throttling before the first outage creates an overage bill.
Understanding the mechanics helps here, especially how overlays measure links and reroute sessions. This explainer on how SD-WAN works covers the control and data plane basics your team should know. Track failover time, cellular data per incident, signal quality trends, and application success on cellular alone. I recommend a monthly forced-failover test at critical sites, because an unused backup path is an assumption, not a control.
7. Multi-Cloud and Cloud On-Ramp Connectivity
Manually building VPN tunnels to every AWS, Azure, and Google Cloud region doesn't scale. Cloud on-ramps automate those connections from the SD-WAN controller, apply consistent routing policy, and let branches reach the nearest suitable cloud entry point without tromboning through one data center.
Say a manufacturer connects plants to production workloads in AWS and analytics in Azure. The controller advertises routes, prioritizes plant systems, and monitors latency to each region so traffic enters cloud where it performs best. A financial firm can do the same for a cloud-hosted analytics platform, while keeping regulated data flows on approved segments.
Automation creates its own risks. A route change can shift traffic into a region with higher egress charges, different security controls, or data residency problems. Model egress cost per region before you enable automated on-ramps, and use naming and tagging standards across clouds so policy objects stay readable six months later.
- Verify provider routing guidance: Follow each cloud provider's documented practices for gateways, route limits, and failover.
- Measure region latency: Compare site-to-region latency and loss weekly, not only at design time.
- Segment by workload: Keep production, analytics, backup, and development traffic in separate policy classes.
- Audit route changes: Log who changed an on-ramp policy and which prefixes moved.
This pattern fits a broader multi-cloud strategy only when network, cloud, and security teams share the design. Track cloud egress spend, application response time by region, tunnel availability, and time to provision a new region. If provisioning gets faster but egress becomes unpredictable, tighten policy before expanding.
8. Voice, Video, and Unified Communications Assurance
Users forgive a slow file transfer. They don't forgive choppy calls. This pattern protects VoIP, video conferencing, and contact center traffic by measuring jitter, latency, and loss on every path and steering real-time sessions to the cleanest link available.
A healthcare contact center, for example, can keep cloud UCaaS calls on the best broadband path during congestion and move them to a second circuit or LTE when jitter rises. A global enterprise migrating from an on-premises PBX to cloud calling can use SD-WAN QoS to protect voice while bulk traffic uses remaining capacity. The platform cannot fix two bad underlay links, poor Wi-Fi, or a headset problem, so isolate the fault domain before you blame routing.
Start with a baseline. Measure jitter, loss, MOS or equivalent call quality scores, and user reports by site for at least a full business cycle. Then align SD-WAN QoS classes with your UCaaS vendor's recommended markings and ports, and make sure LAN switches and Wi-Fi honor the same priorities.
Ongoing Assurance
Use synthetic probing to the UCaaS service so you detect degradation before users open tickets. Review call quality by site, carrier, and time of day every month, and adjust thresholds when traffic patterns change. Test whether an active call survives a link failure, because fast failover for new sessions is not the same as session preservation.
Judge this pattern by completed, intelligible calls during congestion. A green WAN dashboard with unhappy callers means your KPI is measuring the wrong thing.
Track call setup success, jitter, loss, mean time to diagnose voice tickets, and quality during failover events.
SD-WAN Use Cases at a Glance
| Use Case | Primary Goal | Best Fit For | Key Trade-Off |
|---|---|---|---|
| Hybrid WAN and Transport Bonding for Multi-Site Branches | Combine multiple WAN links for resilient, application-aware connectivity | Multi-site organizations seeking alternatives to MPLS-only networks | Lower costs and improved resilience, but performance depends on carrier quality |
| Cloud-First Direct Internet Access for SaaS and Microsoft 365 | Route cloud traffic directly from branches to reduce latency and backhauling | Organizations with heavy SaaS and cloud collaboration use | Faster cloud access, but each internet exit needs consistent security controls |
| SD-WAN with Integrated Security and SASE Architecture | Unify network connectivity and security policies across sites and users | Distributed or regulated organizations pursuing centralized security and zero trust | Simplified management, but may increase licensing costs and vendor lock-in |
| Retail and Franchise Store Networking with Zero-Touch Provisioning | Standardize and rapidly deploy connectivity across many locations | Retailers and franchises with limited on-site IT support | Faster rollouts and consistent policies, but template errors can affect many stores |
| Healthcare Multi-Site Connectivity with Segmentation and Compliance Controls | Securely connect care sites while prioritizing critical clinical traffic | Healthcare organizations with clinics, hospitals, labs, and medical devices | Stronger segmentation and reliability, but changes require careful validation |
| Cellular and LTE/5G Failover for Remote and Mission-Critical Sites | Provide primary or backup connectivity where wired links are limited or unreliable | Remote, temporary, utility, and other critical sites | Rapid deployment and resilience, but coverage and data costs vary |
| Multi-Cloud and Cloud On-Ramp Connectivity | Automate consistent, direct connectivity between sites and cloud platforms | Organizations running workloads across multiple clouds | Simplified cloud connections, but provider fees and operational complexity can grow |
| Voice, Video, and Unified Communications Assurance | Protect real-time communications with performance-based routing and QoS | Distributed teams using VoIP, video conferencing, or contact centers | Better call quality, but QoS needs careful tuning to avoid affecting other traffic |
Matching the Right SD-WAN Pattern to Your Network
SD-WAN is not one project. It's a set of deployable patterns, and the right starting point depends on which problem costs you the most. Transport bonding addresses expensive, fragile branch circuits. Local breakout fixes SaaS latency. SASE convergence closes policy gaps. Zero-touch templates make retail rollouts repeatable, healthcare segmentation protects regulated flows, cellular keeps remote sites online, cloud on-ramps simplify multi-cloud access, and UC assurance protects the traffic users notice first.
Prioritize by business impact, not by whichever feature a vendor demos best. Baseline current circuit spend, application performance, incident volume, and security effort. Then ask the harder cost question. When does SD-WAN reduce total cost, and when does it move cost into licenses, SSE, monitoring, and managed services? In a 2025 global SD-WAN and SASE survey, cost savings were not the primary adoption driver, and among respondents who cited savings, 82% reported reductions of 5% to 29%. Model DIY, co-managed, fully managed, and SD-WAN plus independent SSE with the same fully loaded categories before you claim a saving.
Pilot with intent. Choose representative sites, pull links, degrade a path, change a policy, and force traffic onto cellular. Measure transaction latency, call quality, EHR or ERP response time, failover behavior, cloud egress, and security visibility, not just bandwidth. Decide who owns policy approval, testing, logging, and rollback before rollout. That governance work sounds slower, but it's what prevents a flexible overlay from becoming an unaudited one.
We follow an Assess, Design, Evaluate, Deploy, and Optimize approach for networking, comparing providers without vendor bias and coordinating rollout across sites, wireless, and cloud. Start with a network assessment tied to one priority pattern, prove it in a pilot, and scale only when the KPIs hold at ordinary sites on ordinary days. That's how SD-WAN use cases become operating results rather than another overlay your team has to work around.
If you're weighing DIY, co-managed, or fully managed SD-WAN across branches, clinics, stores, or cloud workloads, we can assess your current circuits and applications, compare options from our curated ecosystem of 400+ providers, and build a phased roadmap with clear KPIs. Visit MR2 Solutions to start a vendor-neutral network assessment and choose the pattern that fits your highest-impact use case first.