Information Technology Procurement: A Complete Guide
The CIO has four vendor decks open, two competing spreadsheets on the screen, and a Slack thread where the same requirement has been phrased three different ways. One business unit wants speed, another wants customization, and security is asking questions nobody included in the original request. Meanwhile, a renewal date is approaching, but no one can explain what the company already owns, what it uses, or whether the current price still reflects the market.
That is the genuine starting point for information technology procurement. It isn't an administrative exercise that begins when someone requests a quote. It is the discipline that turns fragmented technology demand into a defensible decision, a controlled supplier relationship, and an outcome the business can measure.
Most organizations don't fail at this discipline because they lack people — they fail because the work is scattered. That's where structured support comes in. Information technology procurement services typically span portfolio assessment, requirements definition, provider shortlisting, commercial normalization, contract negotiation, and post-signature governance, delivered either as discrete projects or as an ongoing advisory relationship. The discipline itself and the service engagements that deliver it are both covered here. In our review of mid-market sourcing engagements, the pattern that repeats is the same one an audit turns up first — duplicate subscriptions for overlapping capabilities that no single person could name, because each was bought under a different internal champion. The spend was never hidden; nobody was looking at it as one portfolio.
What IT Procurement Really Looks Like in Modern Organizations
A mid-market company may have separate contracts for cloud infrastructure, managed security, collaboration, connectivity, endpoint devices, software licenses, and specialist consulting. Each purchase may have made sense when someone approved it. The problem appears later, when finance sees duplicate subscriptions, IT finds overlapping capabilities, and the security team inherits suppliers nobody properly reviewed.
The CIO then gets asked three questions at once: What do we spend? Which vendors are strategic? What happens if one of them fails? The answers are often scattered across procurement software, email, spreadsheets, renewal notices, and the memories of people who negotiated the original deals.
Practical rule: If nobody can produce a current view of suppliers, commitments, renewal dates, usage, and accountable owners, the organization doesn't have an IT procurement process. It has a collection of buying habits.
Modern information technology procurement brings that fragmented motion under one sourcing strategy. It starts with a clear business outcome, translates that outcome into requirements, creates a vetted provider shortlist, and compares options using the same criteria. It also maintains a contract library that the CFO can use to understand financial exposure and the CISO can use to verify security obligations.
What information technology procurement services include
A services engagement runs in a repeatable arc. It begins with a current-state inventory: contracts, invoices, entitlements, renewal dates, usage, and the accountable owner for each commitment. That inventory feeds a requirements workshop, where business outcomes get translated into functional, technical, security, and commercial criteria. The advisor then curates a shortlist, normalizes the proposals into one commercial format, supports negotiation with market evidence, and stays involved after signature through renewal governance.
Who performs each step matters. The internal team owns the business outcome and final decision. The advisor supplies market coverage, structured evaluation, benchmarked pricing, and negotiation support — vendor comparisons, evaluation summaries, solution recommendations, cost insights, and an implementation roadmap in a typical deliverable set. One client outcome worth naming: an organization that typically spent eight to twelve months completing an RFP cut the process roughly in half with a structured vendor-neutral engagement, and another reported an 82% faster selection that saved $1,044,000 on a single technology deployment.
The engagements we see succeed start with the inventory, not the RFP. Teams that skip straight to issuing paperwork inherit the incumbent's framing of the problem, and every downstream negotiation inherits it too. For readers weighing whether an advisory engagement fits their situation, a resource like Wisely's consultancy for AI solutions shows how specialist providers structure this kind of support in adjacent categories.
The problem isn't a shortage of vendors
Technology buyers don't need more sales presentations. They need fewer, better-qualified options and a neutral way to compare them. A vendor's demo naturally emphasizes its own strengths, its preferred architecture, and the problems its product is designed to solve. That doesn't make the presentation dishonest. It makes it incomplete.
A brokerage model changes the order of operations. The buyer defines the business problem first. An advisor then curates providers that can address it, normalizes commercial proposals, exposes trade-offs, and keeps the internal team focused on fit, risk, integration, and lifecycle cost.
The procurement function has become strategic
The scale of the category makes informal buying dangerous. Gartner forecast worldwide end-user spending on public-cloud services at $595.7 billion in 2024, rising to a projected $723.4 billion in 2025 — an increase of approximately $127.7 billion, with SaaS alone at $299.1 billion. When one slice of the portfolio moves at that pace, Gartner's public cloud spending forecast makes the point plainly: cloud buying is no longer an infrastructure decision, it is a recurring spend discipline that demands the same rigor as any negotiated contract.
The Congressional Research Service summary of federal IT investment states that the U.S. federal government budgets more than $90 billion each year for information technology investments. The same source describes a category affected by large cost overruns, long delays, and substantial supplier concentration.
That pattern appears in private organizations too. Technology decisions shape operating resilience, employee productivity, customer experience, regulatory exposure, and future switching costs. Procurement must therefore manage more than price. It must manage the quality of the decision.
The Core Discipline Behind Information Technology Procurement
IT procurement is the end-to-end discipline that turns a technology need into a supplier relationship with defined outcomes, defensible economics, and controlled risk. It covers the work before a supplier is selected, the terms that govern the relationship, and the decisions made after implementation.
Generic purchasing usually answers a narrow question: how do we obtain an item or service at an acceptable price? IT procurement answers a harder set of questions. Does the solution fit the operating model? Can it integrate with existing systems? Will the supplier protect sensitive data? Can the organization exit without unacceptable disruption? Will the agreed service levels remain useful after the sales team moves on?
The scope is broad. It includes hardware, software, SaaS, cloud, telecom, managed services, implementation partners, cybersecurity, networking, data center capacity, and specialist expertise. The function must connect business requirements with technical architecture, security review, finance controls, legal terms, and supplier performance.
Types of IT procurement
The category breaks into six distinct types, each with its own evaluation logic:
- Hardware procurement: devices, servers, and endpoints — where lifecycle length, refresh cycles, support windows, and residual value drive the economics.
- Software and SaaS licensing: where renewal mechanics, seat and consumption models, and data portability at exit matter more than the headline subscription price.
- Cloud and infrastructure: where usage-based pricing, egress costs, commitment discounts, and concentration risk dominate — the IaaS market grew 22.5% in 2024 to $171.8 billion, with Amazon, Microsoft, and Google holding roughly 70% combined, per Gartner's IaaS market analysis. Concentration simplifies access to scale, but it does not eliminate the need to negotiate.
- Telecom and connectivity: where multi-year circuit contracts, SLA credits, and geographic coverage constraints limit switching options.
- Managed services: where SLA enforcement, staffing guarantees, scope boundaries, and performance evidence determine whether the contract delivers what the sales deck promised.
- Professional services and implementation: where deliverable definitions, rate cards, change-order controls, and knowledge transfer protect the buyer from an open-ended engagement.
A practical distinction
| Dimension | Generic Purchasing | IT Procurement |
|---|---|---|
| Primary objective | Obtain goods or services | Build a technology relationship that delivers a business outcome |
| Evaluation | Price, availability, and basic specifications | Capability, integration, security, resilience, lifecycle cost, and supplier viability |
| Stakeholders | Requester, purchasing, and finance | CIO, IT, security, legal, finance, users, procurement, and executive sponsors |
| Contract risk | Delivery and payment terms | Data ownership, service levels, access, portability, continuity, renewal, and exit |
| Lifecycle | Purchase and payment | Requirements, sourcing, implementation, adoption, performance, renewal, and retirement |
| Commercial analysis | Quoted unit price | Total cost, usage, pricing model, concessions, and future exposure |
| Decision method | Transaction approval | Structured comparison tied to measurable outcomes |
A disciplined team also separates source-to-contract decisions from procure-to-pay execution. The first determines what to buy, from whom, and under which terms. The second ensures approved purchases, invoices, and payments follow those terms. An AP automation roadmap from Loopfour is useful context for the transactional side, but automation can't repair a weak sourcing decision upstream.
Why concentration changes the stakes
Public procurement illustrates the commercial weight of the category. The federal IT contracting data summarized by the Congressional Research Service shows that the ten largest IT vendors captured 37% of estimated federal IT contract spending from 2017 through 2022. The same source reports that inflation-adjusted IT contract spending grew by 27% between 2017–2018 and 2021–2022.
Those figures point to two practical conclusions. First, IT spend deserves specialist attention because mistakes have a large financial and operational footprint. Second, supplier concentration can weaken a buyer's bargaining power if the organization approaches negotiations without credible alternatives. A vendor-neutral advisor helps create those alternatives before the renewal meeting, not after the incumbent has already shaped the requirements.
The IT Procurement Lifecycle From Requirements to Governance
Every technology purchase should pass through four phases, whether the purchase is a new platform or an expansion of an existing service. The formality can vary. The discipline can't.
Requirements
Start with the business problem, not the supplier category. “We need a new collaboration platform” is a procurement prompt. “We need to reduce communication friction across distributed teams while preserving retention, identity controls, and integration with existing workflows” is a usable business requirement.
Translate the problem into four layers:
- Functional requirements: What must users and administrators be able to do?
- Technical requirements: How must the solution integrate, scale, perform, and operate?
- Security requirements: What controls, evidence, logging, access restrictions, and response obligations are mandatory?
- Commercial requirements: How should the supplier price usage, implementation, support, changes, and exit?
Define success measures before speaking with vendors. A TBaaS advisor should challenge ambiguous requirements, identify dependencies, and prevent one supplier's product terminology from becoming the buyer's specification.
Sourcing and evaluation
A shortlist should be curated against the requirements, not assembled from the first vendors that answer an internet search or sales email. Ask each finalist to demonstrate the same workflows, with the same data assumptions and failure scenarios.
Use weighted scoring, structured demonstrations, security review, implementation planning, customer references, and commercial normalization. A buyer comparing a subscription price from one provider with a bundled managed service price from another isn't comparing offers. It's comparing packaging. Security review belongs in this stage, not after it: in a 2024 global survey of software-supply-chain respondents, a significant share said they were not confident that suppliers had adequate cybersecurity compliance practices — evidence that too many buyers assume supplier security rather than verify it.
The Procright RFP guide for IT buyers provides useful process context for teams that still need a formal RFP. The stronger approach is to use the RFP as one controlled instrument inside a broader decision process, not as a substitute for market understanding.
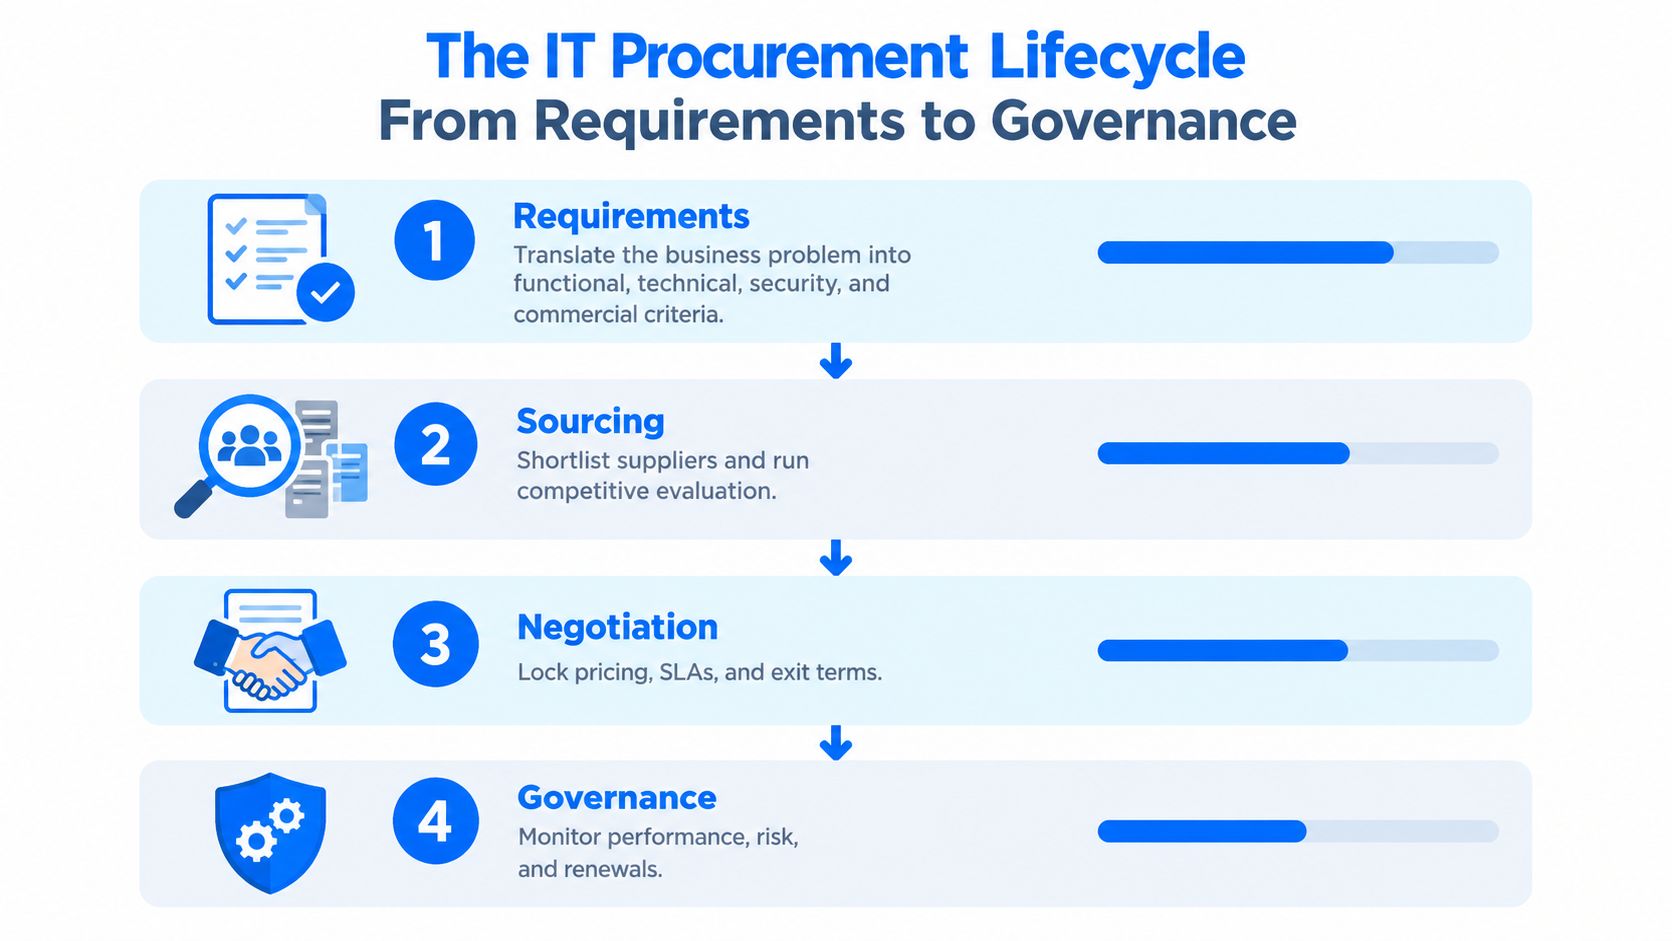
Contracting
A signed order form isn't a finished procurement outcome. The contract must establish service levels, data ownership, security responsibilities, support escalation, pricing mechanics, audit rights, subcontractor controls, change procedures, and termination assistance.
Pay particular attention to renewal language. Automatic renewal, minimum commitments, usage bands, annual uplifts, implementation charges, and professional-services rates can determine the actual economics more than the initial discount. Contract redlines should be reviewed by the people who will operate the service, not only by legal counsel.
A technology due diligence checklist can help teams organize the technical and operational questions that are easy to miss during commercial negotiations.
Governance
Governance begins when the contract is signed. Assign an owner, establish a review cadence, monitor adoption and service performance, track spend against entitlement, and record unresolved issues. Schedule a renewal review early enough to create choices.
A brokerage model remains involved through lifecycle checkpoints. It can compare actual performance with contract commitments, identify scope creep, test whether the supplier's pricing still fits the market, and prepare an exit or renegotiation plan before the renewal deadline turns into a forced decision.
Why a Vendor-Neutral Brokerage Model Changes the Game
Traditional RFPs assume that the buyer can define the market, write a neutral specification, attract the right suppliers, compare responses, and negotiate from a position of knowledge. That works when the category is stable and the requirements are clear. It performs poorly when the buyer is navigating cloud architecture, cybersecurity, AI, connectivity, or a multi-vendor transformation.
The issue isn't that RFPs are useless. The issue is that they often begin too late and ask vendors to define the solution space. Each supplier responds through its own commercial lens. The buyer receives polished answers, but not necessarily a reliable comparison.
TBaaS removes noise without removing control. The internal team still owns the decision. The brokerage curates the market, structures the evaluation, normalizes proposals, and pressures tests the trade-offs so the buyer can concentrate on business fit and risk.
| Dimension | Traditional RFP | Vendor-Neutral Brokerage (TBaaS) |
|---|---|---|
| Market view | Buyer identifies and invites suppliers | Advisor curates providers against stated requirements |
| Comparison | Responses arrive in different formats | Capabilities, assumptions, pricing, and risks are normalized |
| Bias | Vendor narratives shape the evaluation | Buyer outcomes shape the shortlist |
| Internal effort | Stakeholders manage sourcing administration and sales activity | Stakeholders focus on fit, governance, and decision quality |
| Negotiation | Often begins after a preferred supplier emerges | Commercial pressure starts with credible alternatives |
| Lifecycle | Frequently ends at signature | Extends through implementation, performance, and renewal |
| Decision quality | Strongly influenced by presentation quality | Anchored to evidence, requirements, and total outcomes |
How to test neutrality
Ask the intermediary how it gets paid. A reseller margin or referral incentive can compromise the shortlist even when the advisor uses neutral language. Buyers should also ask to see how pricing data is sourced, how conflicts are disclosed, and whether references include clients who chose not to buy from a recommended provider.
The same principle applies in specialized sourcing. If a team needs to browse teleoperation capture data, it should define the data, quality, rights, and operating requirements before selecting a provider. The lesson extends across IT categories: the buyer should control the criteria, not inherit them from the seller.
A focused cloud services brokerage market overview can help teams understand why cloud decisions often require coordination across providers, architecture, security, operations, and contract economics. Brokerage is valuable when it produces a clearer decision, not when it adds another layer of meetings.
Cost Optimization Strategies That Actually Move the Needle
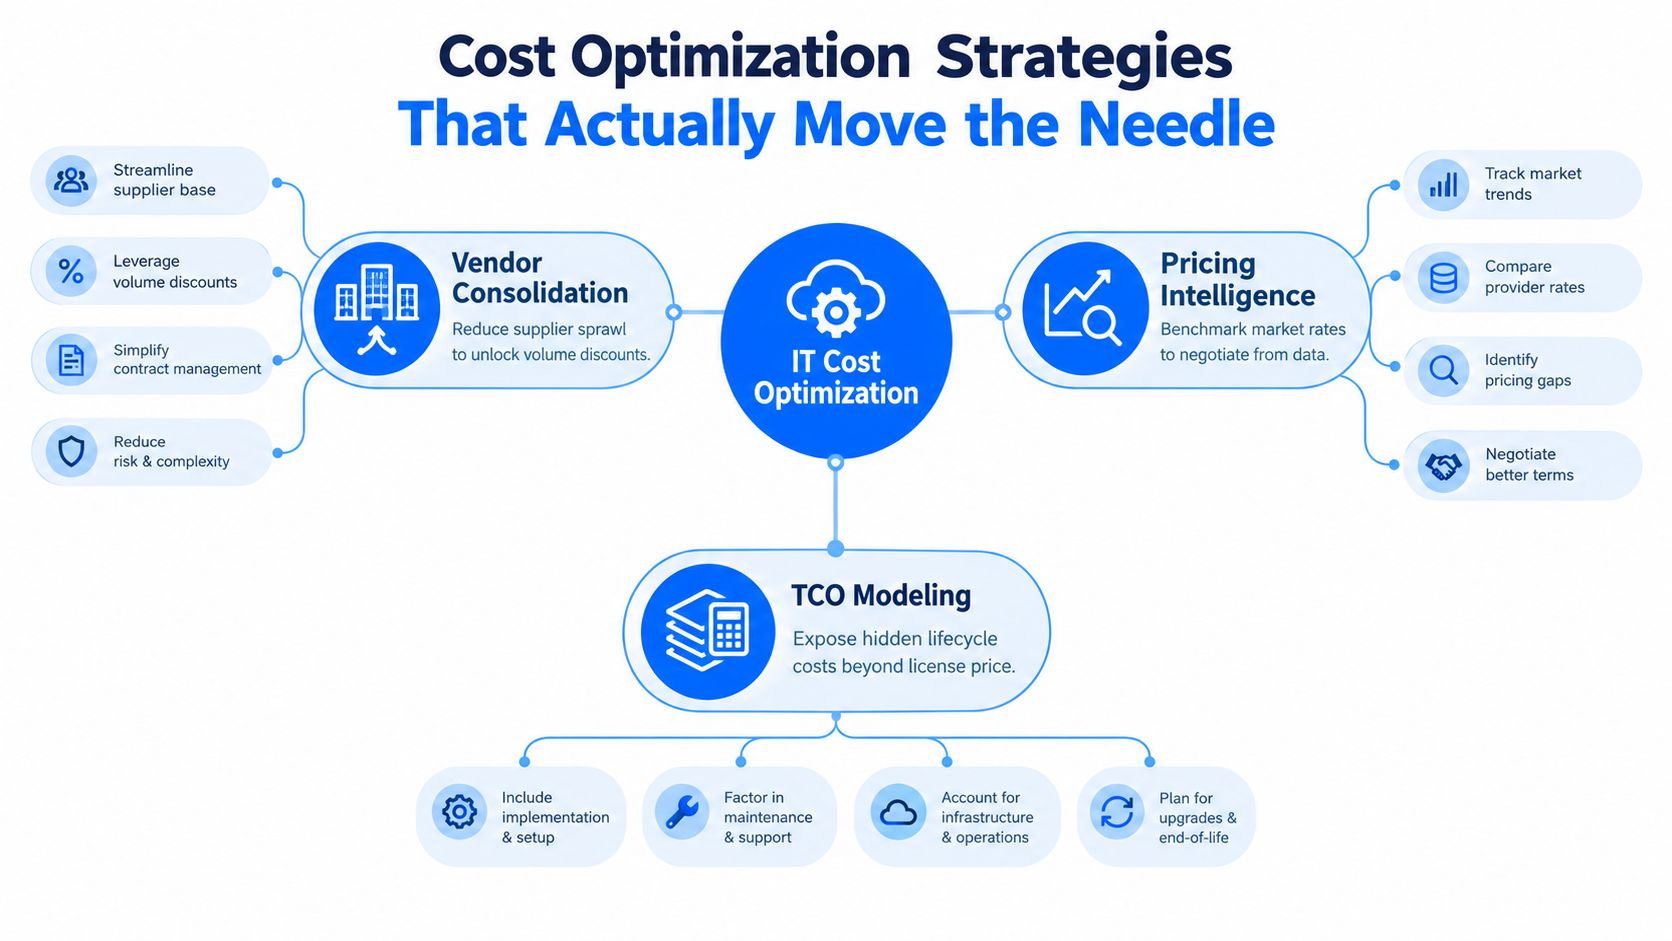
Most IT cost programs start with a request for a better discount. That is usually the smallest available lever. The larger opportunities sit in duplicated suppliers, unused capacity, unfavorable pricing structures, fragmented support, and lifecycle costs hidden outside the license line.
Consolidate with a reason
Vendor reduction can improve economics and simplify operations, but consolidation isn't automatically good. A single supplier may introduce dependency, weaken resilience, or force the organization into capabilities it doesn't need.
The enterprise IT sourcing study reported by NPI Research found that 66% of large enterprises concentrate 80% of IT spend with 25 or fewer vendors, while 82% are actively pursuing supplier reduction. Use that direction intelligently. Consolidate redundant tools and contracts where the operating model supports it, but preserve credible alternatives for critical services.
Model total cost, not just price
A license quote can look attractive while implementation, integration, data migration, support, training, internal administration, and exit work make the solution expensive. TCO modeling should include the cost of the surrounding operating model, not just the supplier's invoice.
Build scenarios for the full contract life. Test what happens when usage rises, requirements change, service levels increase, or the organization needs to move data to another provider. Independent benchmarking guidance on TCO benchmarking for technology decisions reinforces the need to evaluate volumes, service levels, operating model, and delivery mix rather than relying on rate comparisons alone.
Bring market evidence into the room
Pricing intelligence changes the negotiation from “Can you improve this quote?” to “How does this proposal compare with relevant market transactions?” The useful benchmark matches the buyer's size, industry, geography, product scope, volumes, term, and service assumptions.
One enterprise pricing-intelligence source reports that organizations integrating pricing intelligence into every renewal process achieve 18% to 26% better pricing outcomes, based on benchmarks built from actual enterprise contracts matched to those factors. See the pricing intelligence guidance for new purchase evaluation for the methodology and application.
A brokerage operationalizes all three levers. It aggregates the portfolio, finds overlapping capabilities, compares total cost, and gives negotiators a defensible target range. That is more powerful than asking every account executive for one more concession.
For ongoing visibility, technology expense management should connect contracts, invoices, entitlements, usage, owners, and renewal dates. Without that data foundation, cost optimization becomes a series of isolated negotiation events.
Procuring AI and Automation Without Creating Governance Debt
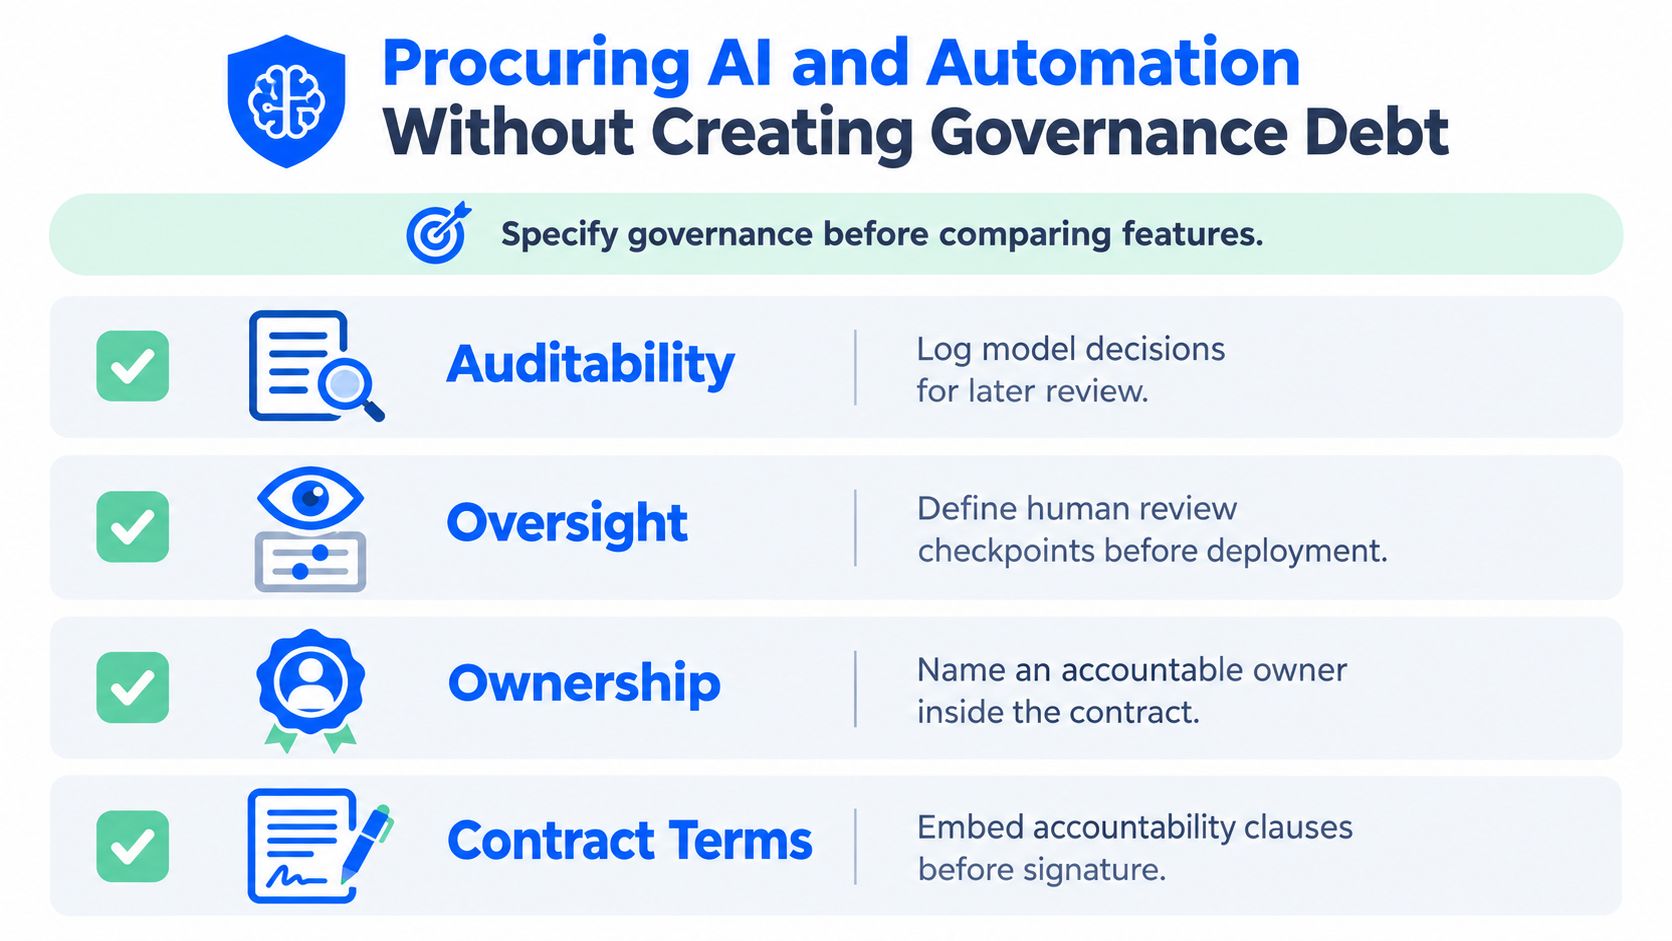
AI procurement is often treated as a feature contest. Buyers compare model quality, automation breadth, integrations, and demo performance, then discover later that nobody defined who can review an automated decision, who owns derived data, or what happens when the vendor changes the model.
The contract must answer those questions before signature. Auditability, human oversight, and accountability aren't optional additions for regulated or high-impact workflows. They're part of the product's operating requirements.
Recent procurement coverage shows why the gap is urgent. The Beroe analysis of global IT sourcing trends reports that only 27% of surveyed organizations have fully embedded an AI strategy across business units, while 37% are comfortable assigning AI agents to execute full end-to-end processes. The same source reports that 83% expect AI agents and automation to break down functional silos.
Specify governance before comparing features
Use the evaluation process to test how the supplier behaves under failure, investigation, and change. Ask for concrete answers to questions such as:
- Data ownership: Who owns prompts, inputs, outputs, fine-tunes, embeddings, and derived datasets?
- Model control: Will the supplier notify the buyer about model changes, deprecation, retraining, or material behavior shifts?
- Auditability: What logs exist, how long are they retained, and can the buyer export them for review?
- Human oversight: Which decisions require review, approval, escalation, or the ability to override?
- Legal response: What happens when the supplier receives a subpoena, government request, or rights complaint involving buyer data?
- Exit and portability: Can the buyer retrieve data, configurations, prompts, workflows, and relevant history in a usable format?
Name the owner
An AI contract should identify the accountable business owner, technical owner, security reviewer, and escalation authority. “The AI team” isn't an owner. It is an invitation for responsibility to disappear between departments.
Treat AI clauses as a baseline for enterprise IT contracts. A provider that won't explain its data handling, logging, model changes, or exit process hasn't completed its product demonstration. It has shown you the happy path.
Building a Procurement Governance Framework That Lasts
Governance fails when it lives in a policy document nobody consults during an actual purchase. The durable alternative is to put controls inside the workflow, where a request can't progress without the information and approvals required for its risk level.
Decision rights
Define who can approve a purchase, renewal, exception, architecture change, security risk, and contract deviation. The exact thresholds should reflect the organization's size and risk appetite, but the rule should be visible before a negotiation starts.
The decision-rights map should answer practical questions:
- Who owns the business case?
- Who can approve a nonstandard security position?
- Who can accept a service-level exception?
- Who must approve an automatic renewal?
- Who has authority to sign a contract with material data or exit risk?
Review cadence
A supplier review should happen often enough to catch problems while the buyer still has options. Review adoption, incidents, service levels, open remediation items, invoice accuracy, consumption, roadmap changes, and upcoming renewal dates.
Quarterly reviews are useful for strategic suppliers when the contract and operating risk justify them. Less critical suppliers may need a lighter cadence. The important point is that the cadence is assigned, recorded, and connected to action.
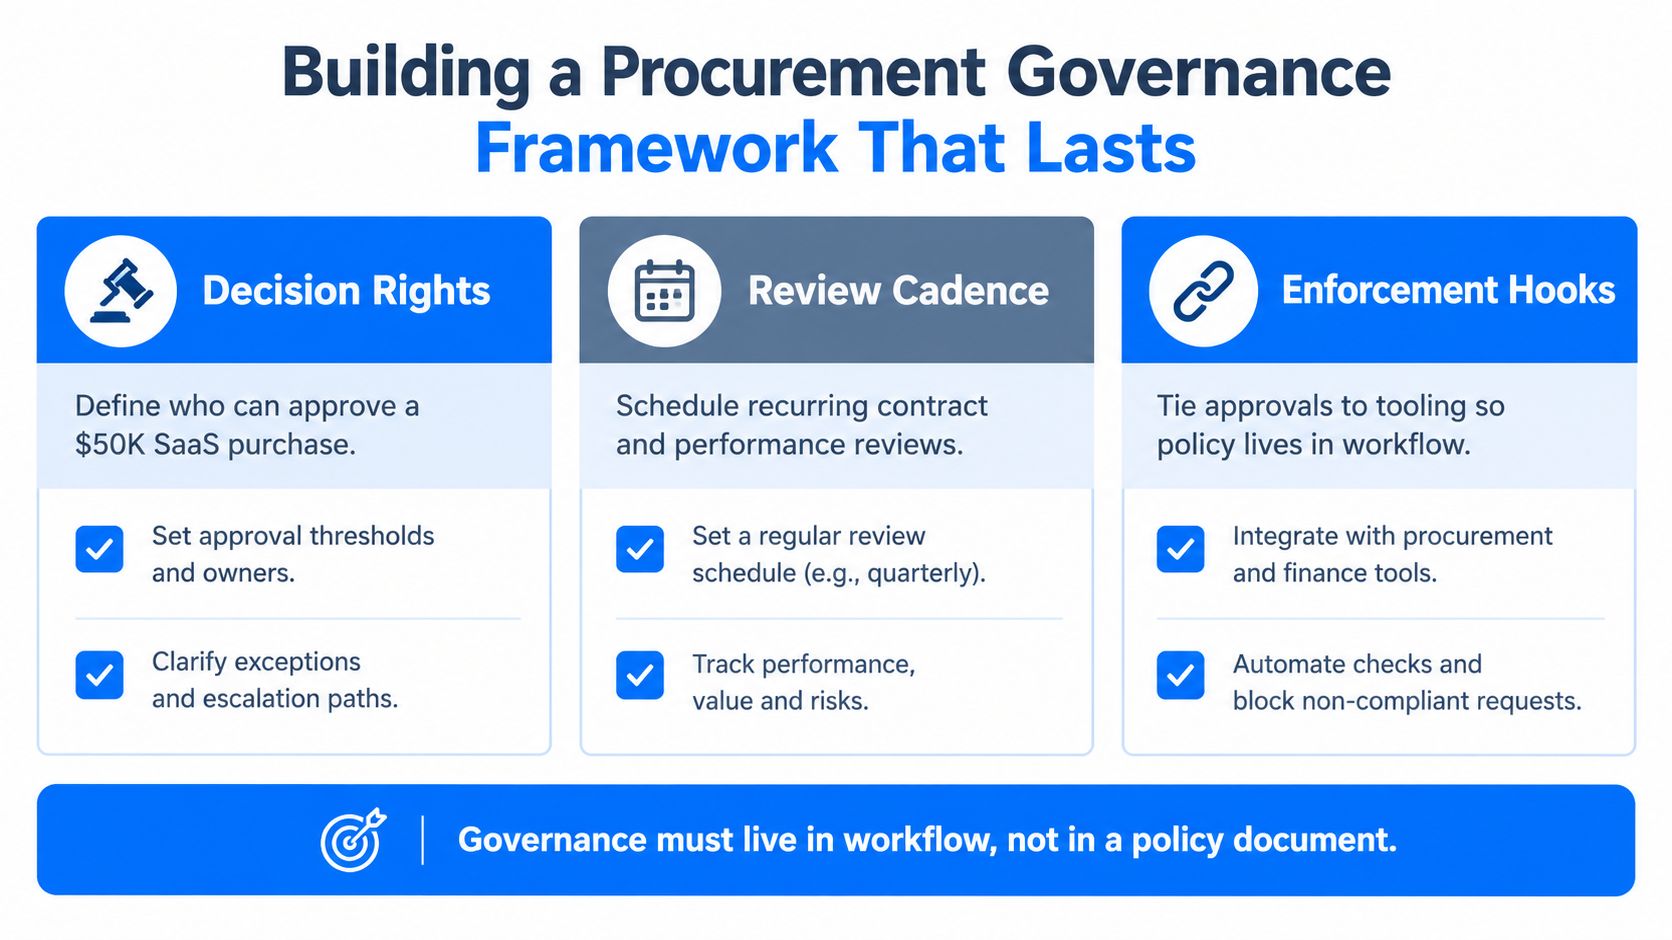
Enforcement hooks
A policy without an enforcement mechanism is advice. Tie procurement controls to intake, contract management, finance approval, identity systems, and renewal alerts. Require an owner and an approved contract before a supplier can receive payment. Require a review before an auto-renewal can proceed.
The framework should discipline decisions in the room, not produce a binder for the shelf.
A vendor-neutral brokerage can sustain this model after signature by monitoring usage, flagging scope creep, benchmarking renewal pricing, and coordinating reviews across internal stakeholders. That post-signature role matters because governance degrades quickly when nobody owns the relationship between formal checkpoints.
Frequently Asked Questions
What does information technology procurement include?
Information technology procurement covers the full path from a technology need to a governed supplier relationship. That includes requirements definition, provider shortlisting and evaluation, contract negotiation, implementation coordination, and post-signature governance of performance, spend, and renewals. It spans hardware, software and SaaS, cloud, connectivity, managed services, and specialist consulting.
What are types of procurement?
The main types are hardware, software and SaaS licensing, cloud and infrastructure, telecom and connectivity, managed services, and professional services. Each carries distinct evaluation criteria: hardware turns on lifecycle and refresh economics, SaaS on renewal mechanics and data portability, and managed services on SLA enforcement and scope control. The types section above details the specific considerations for each category.
What are digital procurement systems?
Digital procurement systems are the software platforms that manage sourcing, contracts, supplier data, invoices, and spend analysis in one place. They range from e-procurement and contract lifecycle management tools to technology expense management platforms that track usage, entitlements, and renewal dates. The system supports the process — it does not replace the evaluation judgment that determines a good purchase.
How is IT procurement different from purchasing?
Purchasing answers a transactional question: how do we obtain an item at an acceptable price. IT procurement answers a broader one: how do we choose, contract, and govern a supplier relationship that delivers a business outcome with acceptable risk. The difference shows up in contract terms like data ownership, exit rights, and service levels — issues a purchase order never addresses.
What do IT procurement services cover?
These services typically cover portfolio assessment, requirements definition, provider shortlisting, commercial normalization, negotiation support, and renewal governance. An advisor performs the market-side work while the internal team retains the decision. In a structured vendor-neutral engagement, deliverables usually include vendor comparisons, evaluation summaries, cost insights, and an implementation roadmap.
Putting It All Together and Your Next Move
Information technology procurement converts fragmented technology spending into governed commitments tied to business outcomes. The operating sequence is straightforward: define the result before discussing products, compare providers against common criteria, negotiate the full lifecycle relationship, and keep governing the contract after signature.
In our review, two checklist items below get skipped more than any others: Alternatives and Renewal. Teams default to the incumbent's shortlist and let the renewal date arrive on the supplier's timetable. Hypothetically, consider a scenario where a connectivity contract auto-renews weeks after a review meeting is scheduled, locking in pricing that has drifted well above market for another full term. The review existed in policy; the trigger didn't exist in the calendar. Avoiding that outcome requires treating the renewal date as a project milestone, not an administrative footnote.
A vendor-neutral brokerage makes the sequence practical for teams that don't have the time, market coverage, or specialist capacity to manage every category alone. It curates options, structures comparisons, brings commercial evidence into negotiations, and maintains attention on implementation and renewal rather than treating the signed contract as the finish line.
Run this checklist against your next technology decision:
- Outcome: Have you described the business result before naming a product or supplier?
- Requirements: Have IT, security, finance, legal, and users agreed on the functional and nonfunctional criteria?
- Alternatives: Can you explain why the shortlist includes these providers and excludes others?
- Economics: Have you modeled implementation, integration, support, usage, renewal, and exit?
- Governance: Are decision rights, owners, review dates, service measures, and escalation paths documented?
- Renewal: Is there a trigger that starts the review before the supplier controls the timetable?
- Evidence: What pricing and performance data will you use to test the supplier's position?
Procurement improves through repetition. Each well-run decision strengthens the vendor bench, sharpens the contract library, improves internal requirements, and gives the next negotiation better evidence. Treating IT procurement as an ordering function leaves that advantage unused.
MR2 Solutions helps organizations evaluate, procure, implement, and govern IT through its vendor-neutral Technology Brokerage-as-a-Service framework, including structured provider comparisons, contract support, and ongoing optimization. Visit MR2 Solutions to discuss your next technology decision with an advisor who can connect business outcomes to the right sourcing process.